ISO 31000 – Risk management framework for organizations in Kuwait
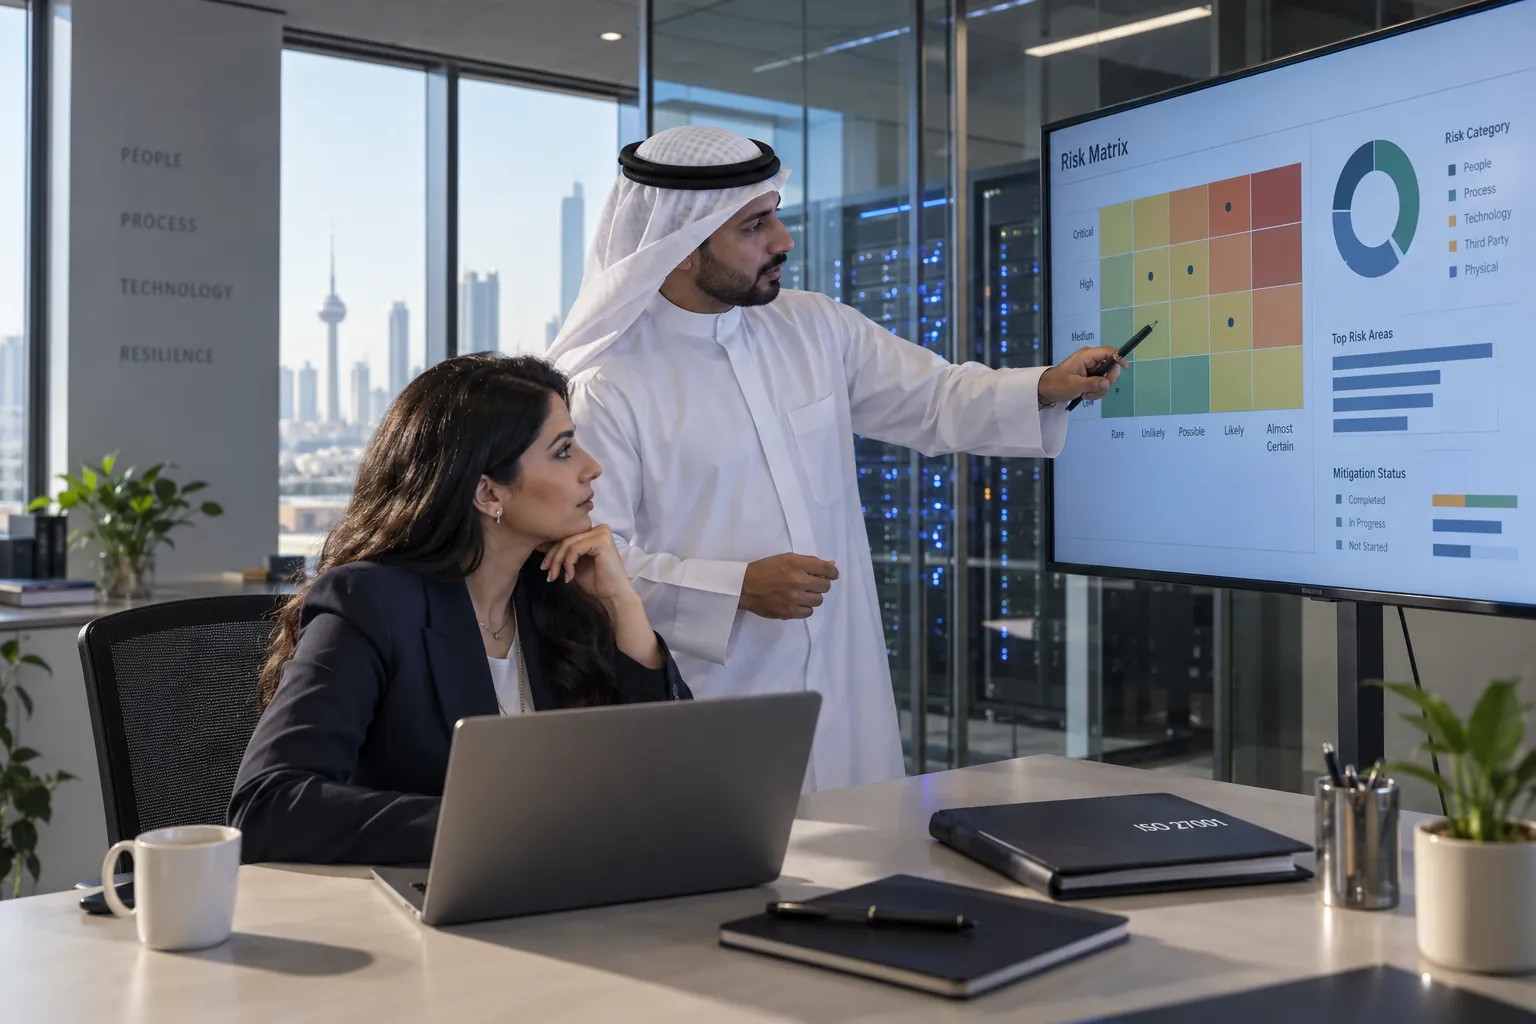
Risk management is a fundamental element in the success of modern organizations, as it helps to identify and analyze potential risks that may affect the operations or strategic goals of the organization, and to take appropriate actions to address them.
ISO 31000 provides a systematic framework that helps organizations develop an effective system for managing institutional risk, contributing to improved decision-making, reduced potential losses, and enhanced operational stability.
At GCC-CERT, we help organizations in Kuwait develop an integrated risk management framework that complies with the ISO 31000 standard and enhances the organization’s ability to address challenges and opportunities.
Understanding the framework of institutional risk management
ISO 31000 is an international guidance standard for risk management, not a standard against which a certificate of conformity is issued. It provides principles, a framework and a process that help the organization identify, analyze, evaluate and treat risks, and link risk management to governance and decision-making.
What is the ISO 31000 standard?
Why do organizations need risk management?
The importance of institutional risk management
Improving strategic decision-making
Reducing potential losses
Strengthening operational stability
Improving the ability to handle crises
Enhancing confidence among investors and partners
Improving institutional governance
The basic principles of risk management according to ISO 31000
Integrating risk management into institutional processes
Adopting a systematic and organized approach
Involving stakeholders
Making decisions based on information
Continuous improvement
Risk management framework
The ISO 31000 framework includes several key elements such as:
Risk management policy
Governance structure
Identifying risks
Risk analysis
Risk assessment
Follow-up and review
Managing risks and opportunities
Documentation and records
Continuous improvement
Risk management process
Identifying risks
Risk analysis
Risk assessment
Risk Treatment
Monitoring risks
Performance review
Common mistakes in risk management
Lack of a clear framework for risk management
Neglecting strategic risks
Failure to update the risk register
Weak participation of senior management
Focusing on documentation without implementation
How does GCC-CERT help you with the ISO 31000 project?
Practical support from the beginning until readiness
It is an international guidance standard that provides principles and a framework for managing risk within the organization.
Is it a certificate like the rest of the ISO certificates?
ISO 31000 provides a framework and guidelines for risk management.
Can it be combined with ISO 9001?
Yes, it can be integrated with other management systems.
How long does the application take?
It depends on the size of the organization and the complexity of the operations.
Start developing a risk management system in your organization with GCC-CERT
If your organization wishes to improve its risk management capability, enhance operational stability, and make more informed decisions, the GCC-CERT team is ready to help you develop an effective risk management framework in accordance with ISO 31000.